 SaolixGroup
Saolix K2M. Know who you are onboarding, and keep the record.
Known2Me is eKYC and identity verification built as one system: consent, capture, checks, human review, appeals and audit. It is not a chain of separate vendors stitched together.
Pre-release The simulator and sample report show how K2M is designed to work, with fictional applicants; parts are not yet in the current release. The screenshots below are from K2M itself.
Verify the person, not just the document, and keep the record that proves it.
Identity checks are usually assembled from parts: an OCR tool here, a liveness vendor there, a spreadsheet for the audit. The gaps between them are where fraud gets in, genuine customers drop out and compliance fails. K2M handles the whole journey in one place. It asks for consent before any biometric step, captures the document and the person, and checks the identity against earlier applications. Decisions go to human reviewers, with a second reviewer required for high-risk sessions; evidence custody, admin actions and session history are written to audit tables protected by database triggers, and a rejected session can be appealed.
Automated checks inform. Reviewers decide.
Automated checks score each capture against minimum thresholds. Reviewers make the decision, and high-risk sessions need a second reviewer.
What K2M does today.
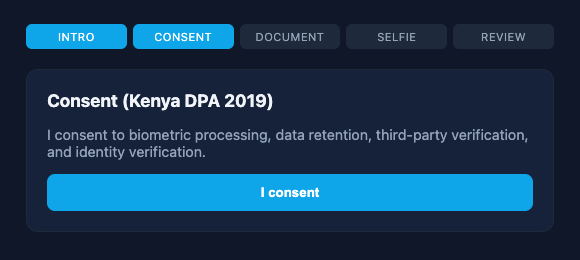
Consent-first capture
A guided flow that records consent before any biometric step, then captures the document and a selfie. The mobile app adds the back of the document and active liveness challenges.
intro · consent · document · selfieDuplicate identity detection
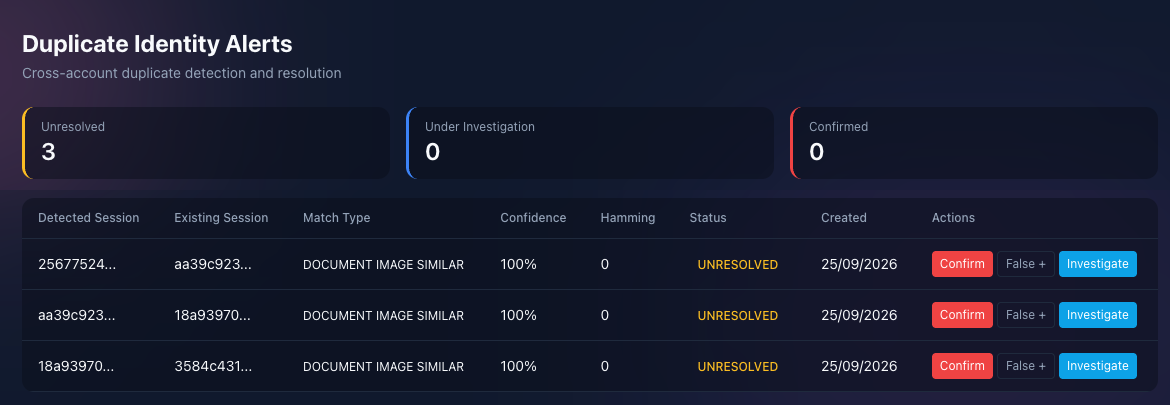
Compares new applications against earlier ones and flags the same document image appearing across different sessions, for a reviewer to confirm or dismiss.
cross-session · reviewer resolvesHuman review with four-eyes
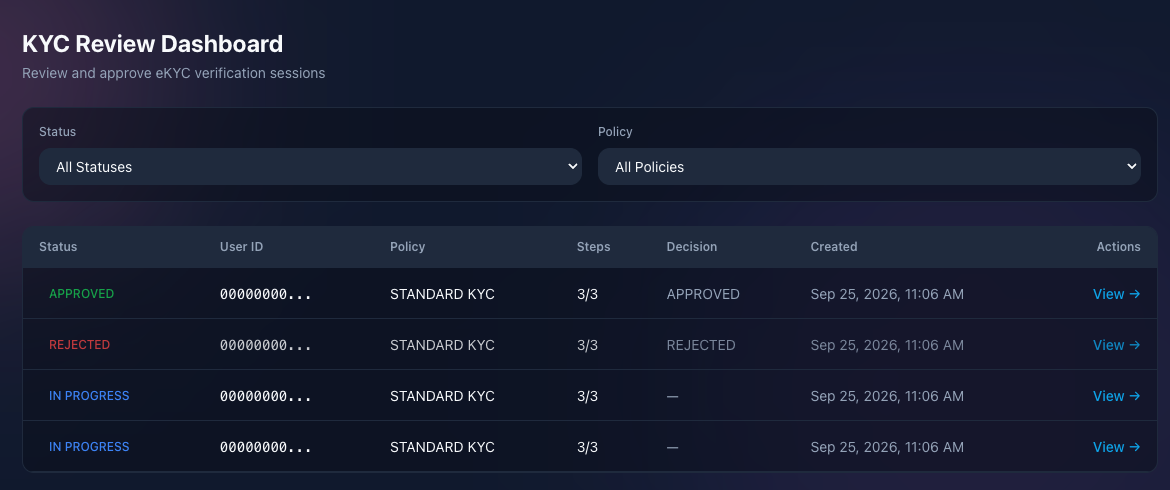
Reviewers approve or reject from one dashboard. For sessions at a high assurance tier, or with a high risk score recorded in the review, any decision needs a second reviewer, and one reviewer cannot give both approvals.
dual approval · policy-basedAudit trail and appeals
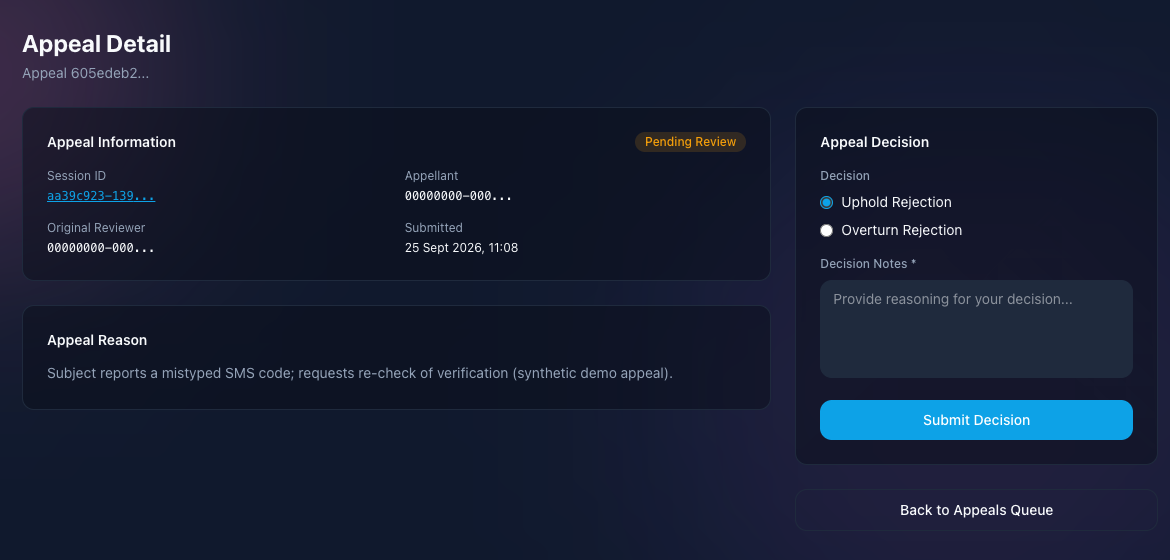
Evidence custody, admin actions and session step history are written to audit tables where database triggers block edits and deletions. Staff can open an appeal against a rejected session; the reviewer who recorded the rejection cannot decide the appeal, and the outcome is recorded with reasoning.
protected audit · appealsSelf-hosted, no third-party KYC vendor.
K2M is built as a container stack you operate.
Don't take our word for it. Inspect it.
Start with any of these.
K2M Simulator
Follow a fictional applicant through K2M's intended design, from consent to decision: the threshold checks, the four-eyes review and the appeal.
Open the simulator ↗ Download · PDF · intended designDesigned report format
The Identity Verification Report K2M is designed to produce, for a fictional applicant: document checks, threshold checks, four-eyes review, appeal and audit timeline. The current release does not yet generate it.
Download the sample → On requestLive walkthrough
We walk you through K2M itself with a synthetic applicant, while you watch.
Book a session ↗Screenshots from K2M itself
Taken from K2M running on our own machines, with synthetic applicants and a specimen ID card. Images are cropped for size.
Further reading.
Identity decisions people can challenge
Hard minimums, two reviewers and a fair appeal in K2M.
AI governanceWhy AI advises and rules decide
The three tests a regulated decision must pass.
ArchitectureThe determinism boundary in practice
How Eagle lets AI help an analyst without ever letting it decide.
Your next chapter.
Let’s build it together.
Explore a product, discuss a project, or find the right expertise. Tell us where you want to go. We’ll help you take the next step.